The cybersecurity industry has always been an arms race. Attackers find new vectors; defenders build new tools; attackers adapt. For decades, the defender's primary weapon was signatures: databases of known malware patterns that antivirus software matched against files. This model worked until attackers discovered polymorphic malware — code that rewrites itself on each execution to evade signature matching. Today, AI has fundamentally shifted the battlefield back toward defenders.
Anomaly Detection at Machine Speed
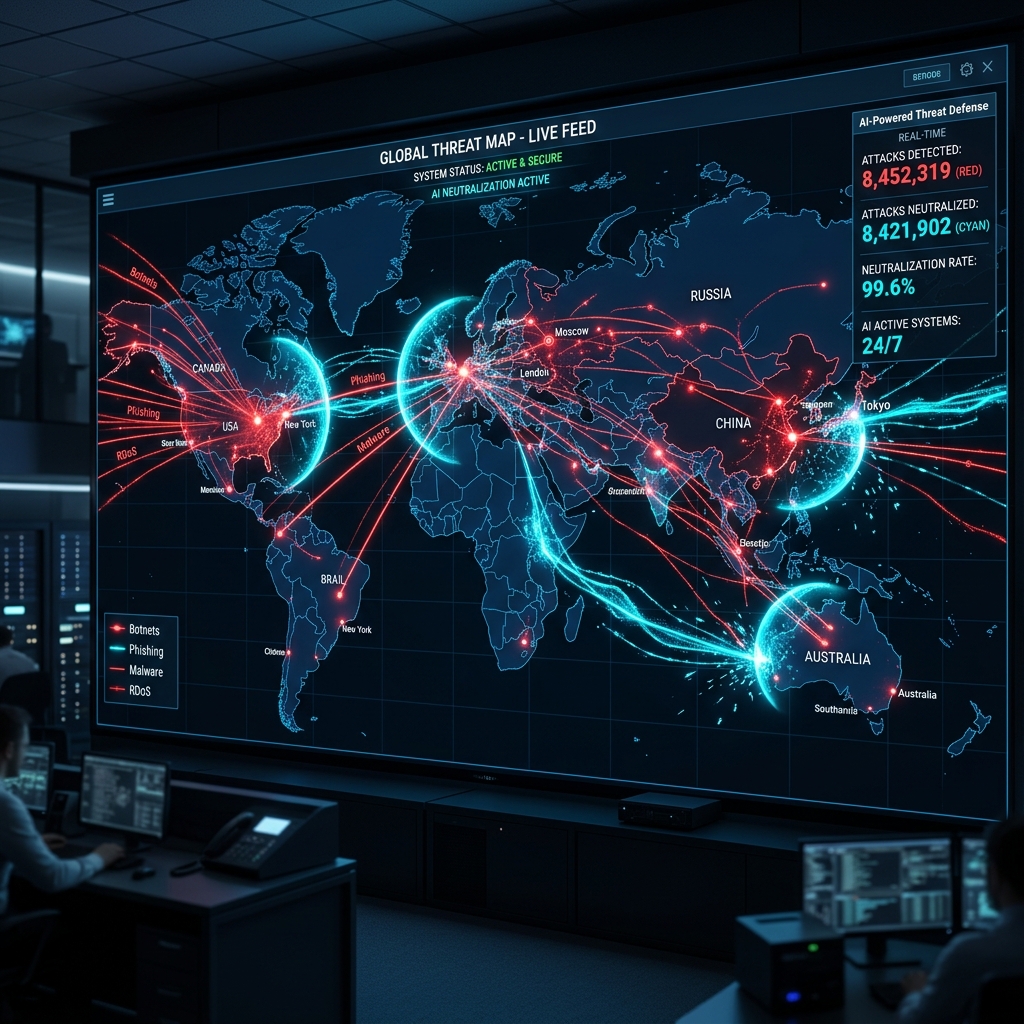
The core advantage AI brings to defence is the ability to establish behavioural baselines and flag deviations faster than any human analyst. A large enterprise network generates millions of log events per hour. No SOC team can manually review this volume. ML models trained on normal network behaviour can identify a lateral movement pattern — an internal service suddenly querying an unusual database at 3 AM — in milliseconds and trigger automated containment: blocking the network path, invalidating the service's credentials, and alerting on-call engineers with full context.
- UEBA (User & Entity Behaviour Analytics): Detects compromised credentials by flagging logins from unusual locations, at unusual times, accessing unusual resources.
- Network traffic analysis: Graph neural networks detect C2 (command and control) beaconing patterns that rule-based tools miss entirely.
- Supply chain monitoring: AI reviews dependency update PRs for suspicious code patterns, obfuscated scripts, or unusual network calls added by a package maintainer.
LLMs in Vulnerability Research
Generative AI has become a force multiplier for security researchers. LLMs trained on CVE databases, exploit code repositories, and vulnerability disclosure reports can now assist analysts in several ways: explaining obfuscated malware samples in plain English, generating hypothetical attack paths through a given system architecture, and writing unit tests that probe boundary conditions likely to contain buffer overflows or injection vulnerabilities.
Google's Project Zero team reported in early 2026 that AI-assisted fuzzing discovered 40% more unique crash sites in tested software compared to traditional fuzzing approaches alone. The AI didn't replace the researcher — it let one researcher cover the ground that previously required a team of five.
The Adversarial Side
It would be naive to discuss AI in cybersecurity without acknowledging that attackers have equal access to these tools. AI-generated phishing emails are now nearly indistinguishable from authentic communications. Automated vulnerability scanners powered by LLMs can probe attack surfaces at scales previously requiring nation-state resources. The defence must be equally AI-powered — which is why organisations relying solely on perimeter firewalls and scheduled antivirus scans are critically exposed in 2026.
Architect This With Binary Froster
Binary Froster builds precision AI integrations, custom web applications, e-commerce platforms, and ERP systems for businesses worldwide. Enjoy 100% IP code ownership, fixed sprint pricing, and direct engineer communication.


